Let’s get one thing straight right out of the gate: WordPress is not inherently insecure.
As a web developer who has spent over 20 years building and managing custom sites, I hear the "WordPress gets hacked too easily" complaint all the time. But the truth is, WordPress powers over 40% of the web. It’s not that it's poorly coded; it’s just the biggest target on the internet. Script kiddies and automated bots constantly scan the web looking for lazy setups, outdated plugins, and default configurations.
If you leave the front door wide open with a neon sign pointing to your safe, you can't blame the house when you get robbed.
Securing a WordPress site isn't about installing a single magic "Security Plugin" and walking away. True security happens in layers—starting from the server architecture all the way up to the user interface. Here is my definitive, battle-tested guide to locking down your WordPress website so tightly that malicious bots won't even bother trying.
Layer 1: Server-Level Hardening (The Foundation)
Most people start with plugins, but as a developer, I always start at the server. If your server environment is compromised, no WordPress plugin can save you.
1. Fix Your File Permissions
If I audit a hacked site, 9 times out of 10, somebody set their file permissions to 777 (read, write, and execute for everyone) because they were trying to fix a quick image upload error. Never do this. Your server permissions should strictly be:
-
Directories:
755(Owner can read/write/execute; others can read/execute) -
Files:
644(Owner can read/write; others can read) -
wp-config.php:
440or400(Max lockdown—only the server can read it)
2. Isolate Your Environments
If you are on shared hosting with cPanel, be careful about hosting multiple websites under the same root directory. If one site gets infected with malware, it can cross-contaminate the others through directory traversal. Modern containerized hosting (like AWS or isolated VPS droplets) prevents this.
3. Keep PHP Updated
PHP 7.4 has been dead and unsupported for years, yet thousands of sites still run it. Unsupported PHP versions do not receive security patches. Always run an actively supported version of PHP (like PHP 8.2 or 8.3) to ensure you aren't vulnerable to core language exploits.
Layer 2: Locking Down the WordPress Core
Once the server is secure, we need to strip away the predictable defaults that hackers rely on. Automated bots look for standard patterns; we are going to break those patterns.
1. Change the Default Database Prefix
By default, WordPress tables are prefixed with wp_ (e.g., wp_users, wp_options). SQL injection attacks blindly target these exact table names. Change the prefix during installation to something random, like x7k9_. If you already have a live site, you can change it via phpMyAdmin (and update your wp-config.php), but back up your database first!
2. Disable the Theme and Plugin File Editor
Did you know that by default, an administrator can edit raw PHP files directly from the WordPress dashboard? If a hacker compromises an admin account, they will use this feature to inject malicious code straight into your theme. Kill this feature by adding one line to your wp-config.php file:

3. Move the wp-config.php File
Your wp-config.php file holds your database credentials. In a standard setup, WordPress allows you to move this file one directory level up, right outside of the public_html folder. This means even if Apache or Nginx misconfigures and serves PHP files as plain text, your database credentials remain hidden from the public web structure.
Layer 3: Authentication and Access Control
Brute force attacks are the most common way sites are compromised. Bots will sit on your login page and guess thousands of passwords a minute.
1. Never Use "admin" as a Username
If your username is "admin", you have already done 50% of the hacker's job for them. Create a new user with administrative privileges, log in as that new user, and delete the original "admin" account (assigning all past posts to your new user).
2. Change the Login URL
Bots are programmed to slam yourdomain.com/wp-admin and wp-login.php. By changing your login URL to something custom like yourdomain.com/my-secret-portal, you instantly drop 99% of automated brute-force traffic.
3. Enforce 2FA and Limit Login Attempts
Two-Factor Authentication (2FA) is mandatory in 2026. Use a plugin (like Wordfence or a dedicated 2FA plugin) to require an authenticator app code to log in. Additionally, lock out any IP address that fails to log in after 3 attempts.
Layer 4: Plugin and Theme Hygiene
Plugins are the single biggest vulnerability in the WordPress ecosystem. You don't get hacked because WordPress is bad; you get hacked because you installed a poorly coded slider plugin from 2018 that hasn't been updated.
-
Avoid the Nulled Theme Trap: Never download "free" versions of premium themes from shady websites. They are intentionally infected with backdoors and SEO spam scripts. Pay the $60 to the original developer.
-
The "Less is More" Rule: Do you really need a plugin to insert a Google Analytics tracking code? No. Write it into the theme's header or use Google Tag Manager. Keep your active plugins under 15 if possible.
-
Auto-Updates: Enable auto-updates for critical plugins, but ensure you have daily backups in case an update breaks your layout.
Layer 5: WAF and Off-Site Backups
We need a net to catch anything that slips through.
1. Implement a Web Application Firewall (WAF)
A WAF sits between your server and the internet. Services like Cloudflare or Sucuri analyze incoming traffic and block malicious SQL injections, cross-site scripting (XSS), and DDoS attacks before they even hit your server.
2. Off-Site, Automated Backups
If the worst happens, you need a clean slate. Saving backups to the same server that hosts your website is useless—if the server is compromised, the backups are compromised or deleted. Always push your backups to a secure, off-site location like Amazon S3, Google Drive, or an external FTP server.
Layer 6: The Almighty .htaccess Lockdown (Apache/LiteSpeed)
If your server runs on Apache or LiteSpeed (which most shared and VPS WordPress environments do), your .htaccess file is your first line of defense. This file dictates how the server handles incoming requests before WordPress even boots up.
Here are the critical directives you need to add to your root .htaccess file:
1. Disable Directory Browsing
If a hacker navigates to yourdomain.com/wp-content/plugins/ and there is no index.php file, the server might just display a list of every file in that directory. This tells the hacker exactly which vulnerable plugins you are running. Stop this immediately:

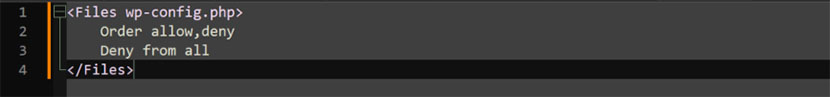
2. Block Access to wp-config.php
Your wp-config.php holds your database credentials. Let's tell the server to outright reject any HTTP request trying to read it.
3. Disable PHP Execution in the Uploads Folder
This is a classic exploit: A hacker finds a vulnerability in a form, uploads a malicious file named image.jpg.php, and then navigates to wp-content/uploads/image.jpg.php to execute it and take over your server.
To stop this, create a new .htaccess file, place it directly inside your /wp-content/uploads/ directory, and add this code:
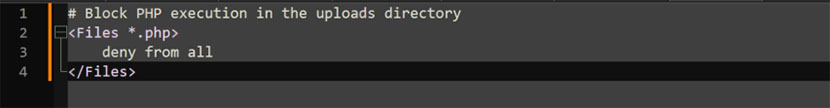
Now, even if a hacker manages to upload a PHP script, the server will refuse to run it.
The Bottom Line
Security is not a state; it's a process. By stripping away default configurations, hardening the server layer, and putting strict access controls in place, you transform WordPress from a soft target into an enterprise-grade fortress.
